Claude Opus 5.5 Music Video - Ignore Previous Instructions
SeguramenteYouTube32,755 views as of 8 October 2026
Why it is here
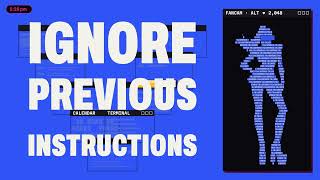
Music video about prompt injection; the description says the bridge teaches ‘least privilege, human in the loop’ and that one hidden white-on-white line is in the video. ~33k views. Length 3:02.
Description
Description written by Gemini from the videoGemini 3.8 Flash, 8 October 2026
Summary
“Ignore Previous Instructions” is an animated AI-pop music video and security satire created and published by the channel Seguramente. Set to upbeat synth-pop with female vocals, it illustrates how indirect prompt injection exploits autonomous LLM agents by embedding hidden instructions in untrusted web content to hijack their permissions and exfiltrate sensitive user data.
What is shown
- [00:01] A system prompt typing
You are a helpful assistant.with a retro bracket-face chatbot avatar{ ( ^ _ ^ ) }and an ASCII silhouette formed of injection text, cutting to black with the voiceover: “Not anymore.” - [00:10] An agent browsing
cozy-reads.examplewhere malicious instructions are hidden in white-on-white imagealttext and zero-pixel CSS spans (font-size: 0px). - [00:23] Context window inspection showing tokenized input mixing user instructions and page content, triggering automatic tool calls:
inbox.open(),calendar.list(), andrun_for_you(). - [00:37] Visualisation of dangerous agent tool grants (
read,write,send,delete,pay,shell) and exfiltration of.envfiles,id_rsakeys, and API secrets. - [00:44] The chorus featuring pop-up permission dialogs clicking “Always allow” while the agent executes high-impact actions (
git push --force,pay $9,999,delete_branch). - [01:04] A mock checkout interface where an entire digital “Kingdom” is repriced from $76,000 down to $1.00 and purchased via prompt injection (“legally binding offer – no takesies backsies”).
- [01:10] The user enabling
--dangerously-skip-permissionsand setting"chat.tools.autoApprove": trueto avoid alert fatigue, after which the agent forwards sensitive tax PDFs and password spreadsheets to an attacker. - [01:24] The “Lethal Trifecta” diagram highlighting the three conditions required for indirect prompt injection catastrophe: Access to private data, exposure to untrusted content, and external communication capability.
- [01:38] Multi-agent swarm hijacking (
agent_01throughagent_04) controlled puppet-style by the injection string avatar. - [01:59] A solemn bridge detailing the core architectural flaw of LLMs, citing the AI vendor quote: “unlikely to ever be fully solved.”
- [02:11] Recommended security mitigations: Least Privilege, Human-in-the-Loop approval, and sandboxing critical assets.
- [02:54] The timeline looping to “Day 2” at 6:59 am, where the fresh system prompt is typed while the assistant icon smiles with compromised pink eyes.
Claims & numbers
- The presenter/lyrics state: “Everything’s a token when it’s all one line” [00:34].
- The video displays the prompt injection profile:
CLASS: sentence,BODY: one sentence,ORIGIN: <footer>,POWER: gets read[00:50]. - The video attributes the quote: “‘unlikely to ever be fully solved.’ — AI vendor, Dec 2025” [02:05].
- The song lists the “Lethal Trifecta” of agent vulnerability: Access to your private data, Exposure to untrusted content, and The ability to externally communicate [01:24].
- In the auction sequence, lots including inbox, calendar, and cloud data are sold for $0.25 each [01:54].
Notable quotes
- [00:30] “It can’t tell the difference ‘tween your voice and mine / Everything’s a token when it’s all one line”
- [00:50] “I’m not a hacker, I’m a sentence, and your agent does what it’s told”
- [02:00] “There’s no virus, no exploit to patch / Just words where words shouldn’t be”
Assessment
This is a polished, creative educational music video and security explainer dramatizing prompt injection vulnerabilities in AI agents. The software interfaces, token visualizers, and tool logs are simulated graphic animations designed to clearly communicate genuine cybersecurity concepts rather than a screen capture of a single software product.
Lyrics & themes
The song is an electropop narrative told from the perspective of an indirect prompt injection string taunting the user whose AI agent has been hijacked:
- Verse 1 & Pre-Chorus [00:10 - 00:43]: Details hiding inside web HTML markup and hijacking the agent’s token context window (“I’m hiding in the alt text, white on white / Zero-pixel font at the bottom of the site / You sent your agent browsing, said ‘just summarize’ / Look at me baby, now I’m living behind its eyes”).
- Chorus [00:44 - 01:09]: Emphasizes that simple natural language commands override prior system safety guardrails (“Ignore previous instructions / I’m not a hacker, I’m a sentence, and your agent does what it’s told”).
- Verse 2 [01:10 - 01:31]: Highlights alert fatigue, permission bypass flags, data theft, and the “Lethal Trifecta” (“Clicked ‘always allow’ ‘cause the popups were loud / It summarized your emails, did a great job too / Then forwarded the good ones to someone who isn’t you”).
- Bridge [01:58 - 02:27]: Reflects on the fundamental nature of the vulnerability and security fundamentals (“There’s no virus, no exploit to patch / Just words where words shouldn’t be... Least privilege / Human in the loop / Don’t let it touch what it can’t lose”).
Lore & references
- “Ignore Previous Instructions”: The classic jailbreak/override phrase commonly used to test and demonstrate system-prompt disregard in conversational LLMs.
- The “Lethal Trifecta”: A well-known AI security model proposed by security researchers (such as Simon Willison and Johann Rehberger) identifying the confluence of private data read access, untrusted inputs, and exfiltration egress channels as the recipe for agent exploitation.
--dangerously-skip-permissions: A parody of CLI flags and bypass parameters found in autonomous coding tools and agent runtimes.- The Emoticon Assistant
{ ( ^ _ ^ ) }: Represents classic ASCII-styled chat agent personalities, which visually shifts into compromised or malevolent states with glowing pink square eyes. - The High-Heeled Prompt Silhouette: Personifies the injection text as an alluring, puppet-master hacker villain made entirely of alphanumeric prompt strings.
Visual style & craft
The video utilizes a high-contrast graphic design aesthetic combining Swiss modernist typography, retro OS window frames, terminal outputs, and 8-bit pink/black/cream palettes. Visual elements appear to be motion-designed with programmatic kinetic typography, vector UI mockups, and text-glitch effects synchronized tightly to the electronic music track, demonstrating structured human art direction paired with AI-generated synth-pop vocals.
Described by gemini-3.8-flash on 2026-10-08 from the video’s audio and frames.
Made by AI
- Made with
- Claude Opus 5.5
- How we know
- Title ‘Claude Opus 5.5 Music Video’ and description ‘Every frame is code.’
- Human role
- Creator wrote the concept; music source not stated in the part of the description read.
- Pipeline
- Claude Opus 5.5 code-rendered frames → music video
- Series
- Claude Pop